Laravel Security Best Practices: Essential Steps to Protect Your Web Applications
Laravel Security Best Practices: Safeguarding Your Web Applications
In today’s digital landscape, security is not an afterthought—it’s a necessity. Laravel, known for its elegant syntax and developer-friendly features, also prioritizes security out of the box. However, even the most robust frameworks require developers to follow best practices to protect applications from evolving threats. Whether you’re building an e-commerce platform or a SaaS tool, here are essential Laravel security practices to keep your application safe and secure.
1. Prevent SQL Injection with Eloquent ORM
Laravel’s Eloquent ORM uses PDO parameter binding to sanitize inputs automatically, making SQL injection attacks far less likely. However, when using raw queries, exercise caution:
// UNSAFE: Avoid this!
$users = DB::select("SELECT * FROM users WHERE email = '$email'");

// SAFE: Use parameter binding
$users = DB::select("SELECT * FROM users WHERE email = ?", [$email]);
Tip: Stick to Eloquent or the query builder for most operations to leverage built-in protections.
2. Defend Against Cross-Site Scripting (XSS)
The Blade templating engine escapes output by default. Only use unescaped output ({!! $content !!}) when you explicitly trust the content:
// Safe (escaped)
{{ $userInput }}

// Risky (unescaped – use only if sanitized)
{!! sanitize($userInput) !!}
Sanitize Input: Use packages like laravel-purifier to clean HTML input before storage.
3. Enable CSRF Protection
Laravel automatically generates CSRF tokens for forms. Always include @csrf in your forms:
<form method="POST">
  @csrf
  <!-- Form fields -->
</form>
For APIs: Exclude routes from CSRF protection in the VerifyCsrfToken.php middleware and use API tokens or OAuth instead.
4. Secure Authentication & Authorization
- Use Built-in Auth Scaffolding:
Laravel’s auth system includes secure password hashing (bcrypt), session management, and throttling.php artisan make:auth - Enforce Authorization Policies: Define policies for roles and permissions using Gates and Policies:
// In AuthServiceProvider.php
Gate::define('edit-post', function ($user, $post) {
    return $user->id === $post->user_id;
});
5. Validate and Sanitize File Uploads
- Restrict file types and sizes:
request()->validate([ 'file' => 'required|file|max:2048|mimes:pdf,docx', ]); - Store files outside the public directory or use Flysystem to secure cloud storage.
- Rename uploaded files to prevent path traversal attacks.
6. Enforce HTTPS in Production
Ensure all traffic uses HTTPS:
- Set
APP_URL=https://yourdomain.comin your.envfile. - Redirect HTTP to HTTPS via middleware:
// In app/Http/Middleware/CheckForMaintenanceMode.php
public function handle($request, Closure $next) {
    if (!$request->secure() && app()->environment('production')) {
        return redirect()->secure($request->getRequestUri());
    }
    return $next($request);
}
7. Protect Sensitive Configuration
- Never commit
.env: Add it to your.gitignore. - Encrypt sensitive data with Laravel’s built-in encryption:
$secret = encrypt($request->secret); - Set
APP_DEBUG=falsein production to avoid exposing errors.
8. Rate Limiting for APIs and Logins
Prevent brute-force attacks using Laravel’s throttle middleware:
Route::post('/login', 'AuthController@login')->middleware('throttle:5,1');
This limits login attempts to 5 tries per minute. For APIs, use Laravel Sanctum or Passport with scopes.
9. Secure Session Management
- Store sessions in a secure driver (e.g., database or Redis).
- Set session cookie security in
config/session.php:'secure' => true, // Send cookies over HTTPS only 'http_only' => true, // Prevent JavaScript access 'same_site' => 'lax',
10. Update Dependencies Regularly
Outdated packages are a common attack vector. Use:
composer update
Leverage tools like Laravel Shift or GitHub’s Dependabot to automate updates.
11. Implement Security Headers
Add middleware to set secure HTTP headers:
// Example Middleware
public function handle($request, Closure $next) {
    $response = $next($request);
    $response->headers->set('X-Content-Type-Options', 'nosniff');
    $response->headers->set('X-Frame-Options', 'DENY');
    $response->headers->set('X-XSS-Protection', '1; mode=block');
    return $response;
}
Alternatively, use the spatie/laravel-security-headers package.
12. Backup Your Data
Use Laravel’s backup package (spatie/laravel-backup) to automate database and file backups. Store backups in secure, off-site locations.
13. Monitor and Log Activity
- Use Laravel’s logging configuration (
config/logging.php) to track errors. - Integrate monitoring tools like Laravel Telescope, Sentry, or Bugsnag.
- Avoid logging sensitive data (e.g., passwords, tokens).
14. Validate All Inputs
Never trust user input! Validate every request, including API endpoints:
// Use Form Requests for complex validation
php artisan make:request StorePostRequest

// In StorePostRequest.php
public function rules() {
    return [
        'title' => 'required|string|max:255',
        'body'  => 'required|string',
    ];
}
Final Thoughts
Laravel provides powerful tools to build secure applications, but their effectiveness depends on how you use them. By following these best practices—validating inputs, securing sessions, updating dependencies, and leveraging built-in features—you’ll significantly reduce vulnerabilities. Stay proactive, audit your code regularly, and keep learning about emerging threats. After all, a secure application is a trustworthy one.
Stay safe, and happy coding! 🛡️
Projects to explore next
Source-code projects from the KritiMyantra catalogue. Check each project's details before buying.
Flask Authentication System (Free Version) - Kritim Yantra
🛠 Features✔ Google & GitHub Authentication✔ User Registration & Login✔ Profile/Dashboard Access✔ Secure & Mi...
Flask Blog CMS with Admin Dashboard — Python Source Code
A Flask-based blogging website with a built-in admin dashboard. Manage articles, images, categories, tags and featured p...
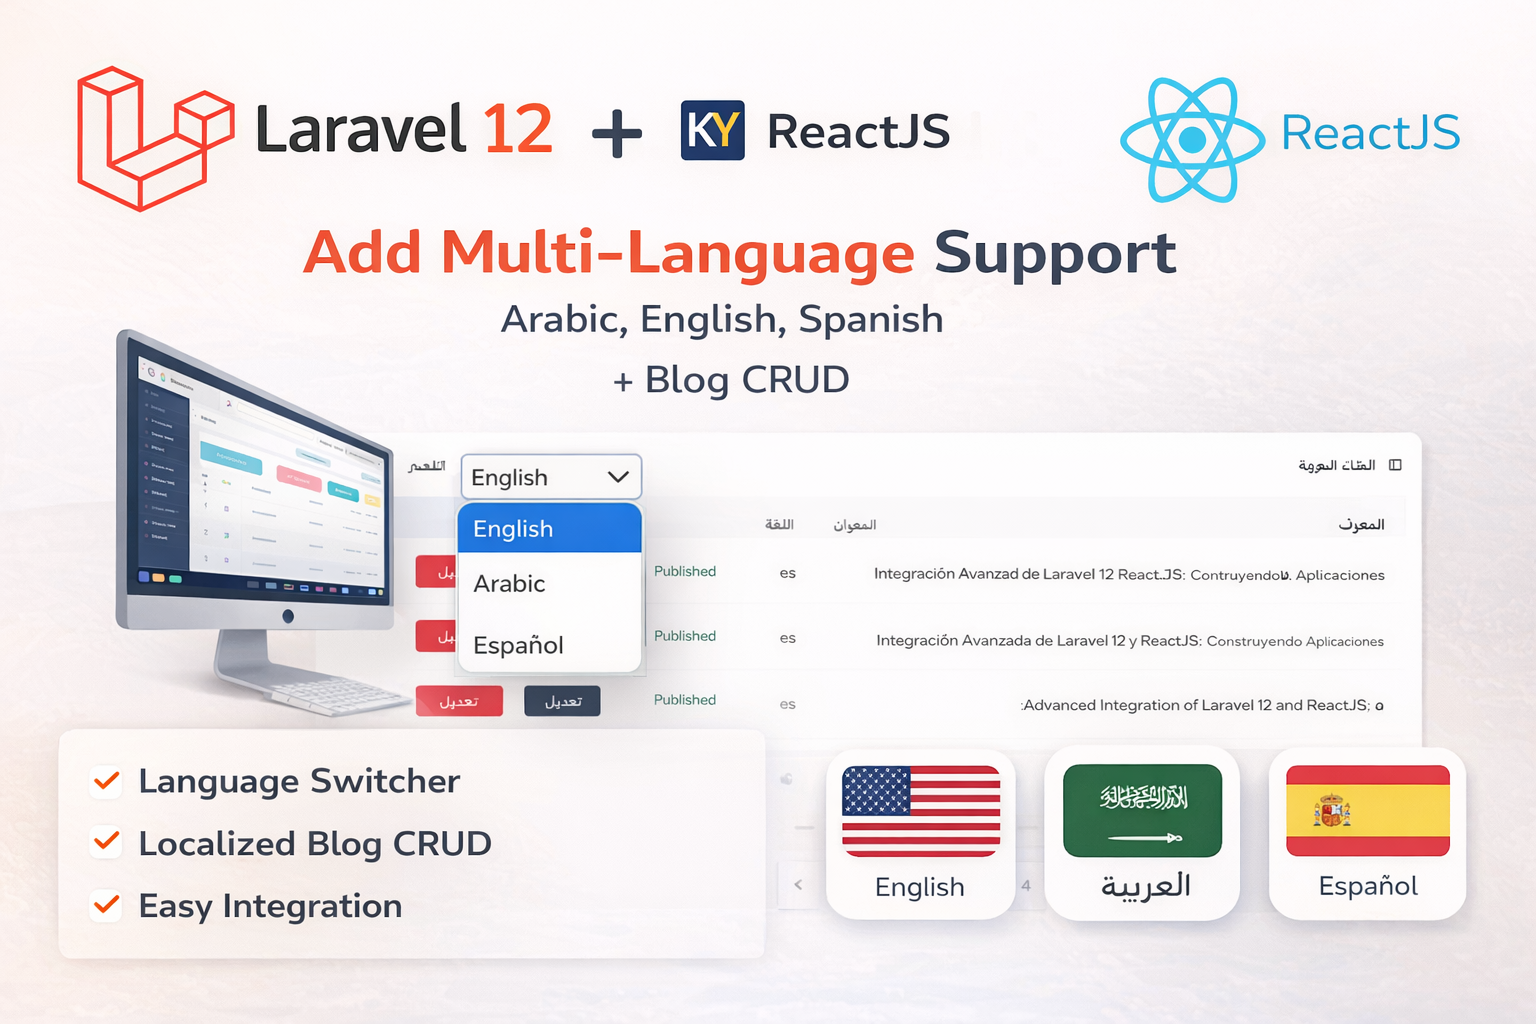
Laravel 12 + ReactJS Starter Kit: Add Multi-Language Support (Arabic, English, Spanish) with Blog CRUD
🚀 Installation & Setup Download & Extract Get the ZIP from kritimyantra.com and extract it. Includes preconfigu...
Laravel 12 CRUD Application with React, InertiaJS & Tailwind CSS
Welcome to this comprehensive guide on building a CRUD application for blog post management using the latest technologies: Laravel...
Laravel 12 Multi-Auth System: Implementing Separate Admin and User Tables
In this blog post, we'll walk through creating a login system in Laravel 12 that supports both admin and user roles using separate...
What Are Laravel 12 Service Providers?
Welcome to this beginner-friendly guide on Laravel 12 Service Providers! If you’re new to Laravel or web development, don’t worry—...
Comments
No comments yet. Be the first to comment.
Sign in to join the discussion.